
WAF and firewall
Stop exploits before they reach the origin.
Every request to a proxied hostname is inspected on our edge nodes in Germany and Spain: OWASP CRS 4.25 and 49 rules of our own, emergency rules for new CVEs, rate limits, IP and country rules and an access gate for admin areas.
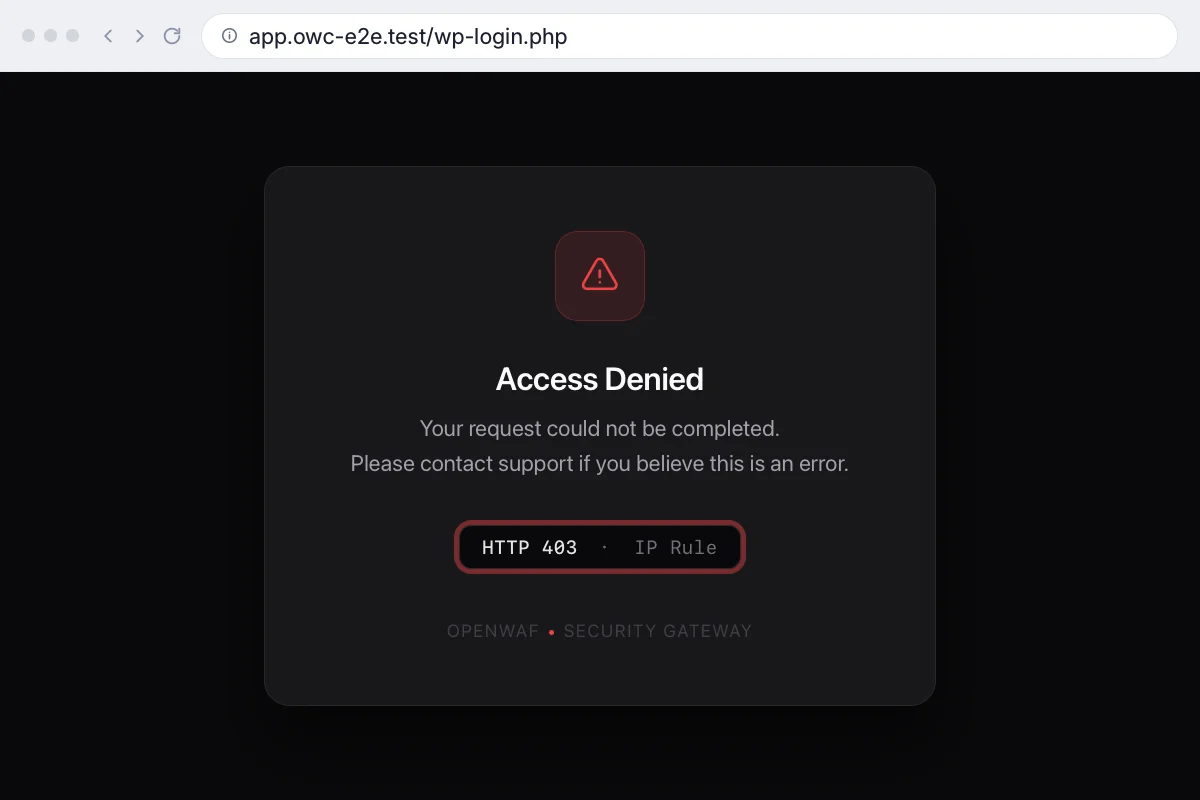
A firewall in front of every client site
Every request to a proxied hostname is inspected on our edge nodes in Germany and Spain: OWASP CRS 4.25 and 49 rules of our own, rate limits, IP and country rules, and an access gate for admin areas.
Web application firewallStop known exploits at the edge, before the origin sees them.
OWASP CRS 4.25 on Coraza plus 49 rules of our own.
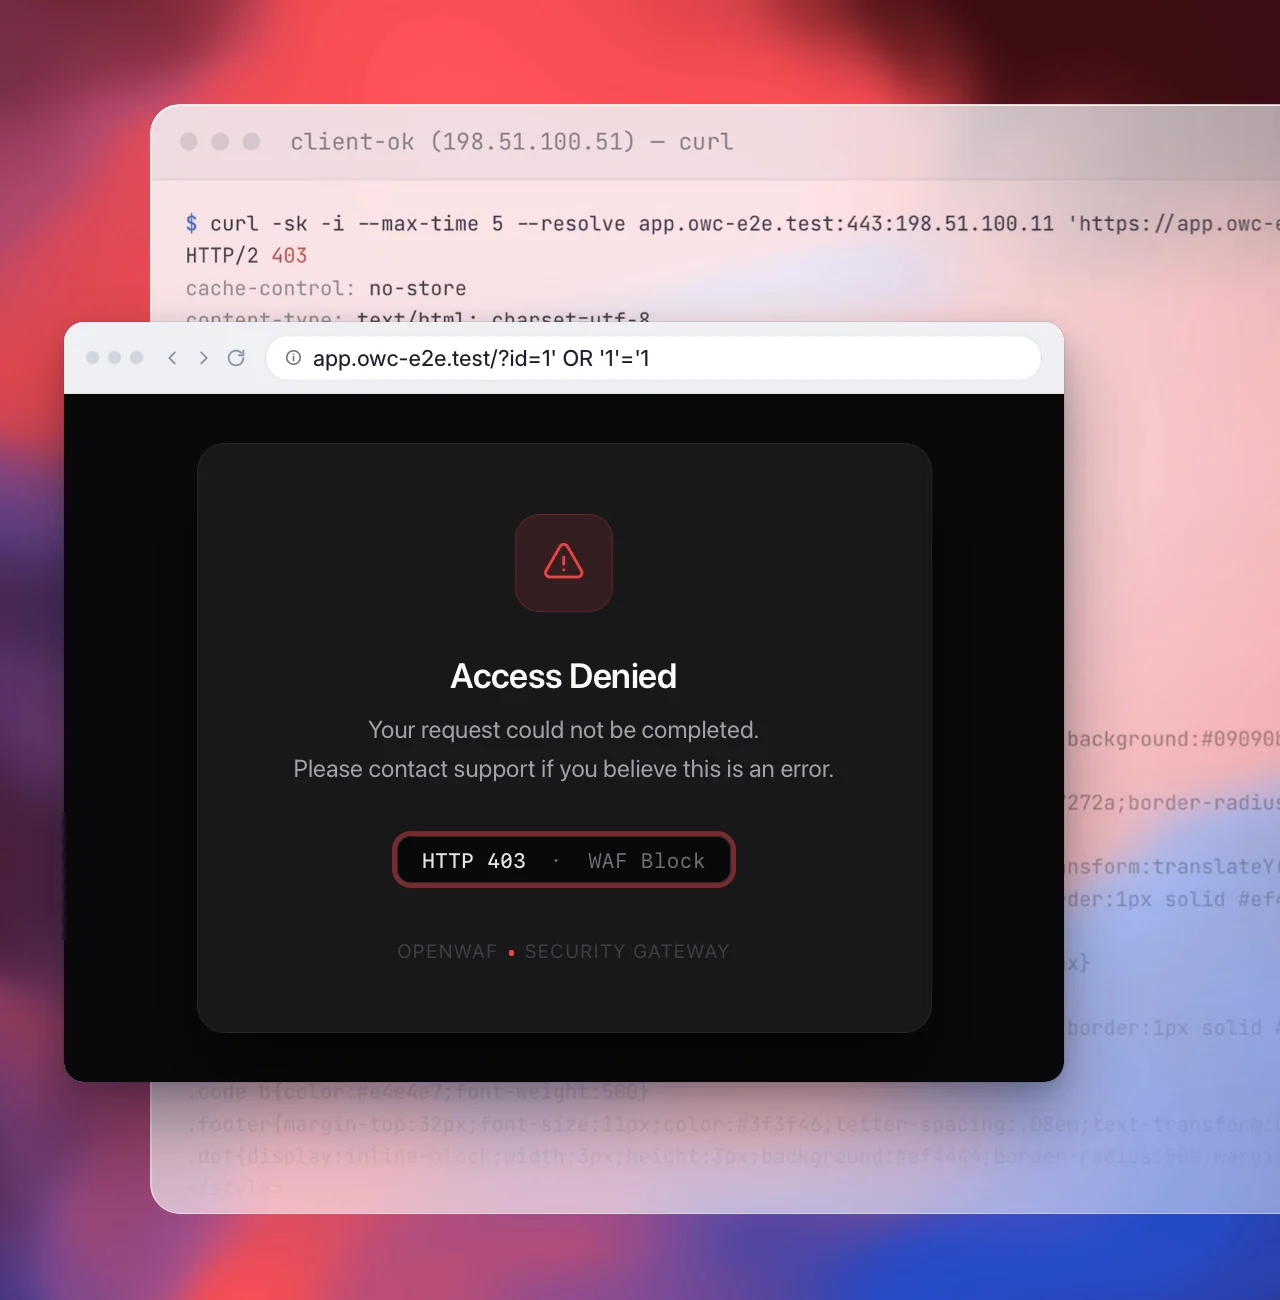
- Rule levels
Off, low, medium or high per site, starting from a WordPress, Next.js or static preset.
- Active, log-only or off
Active mode blocks. Log-only records what would have been blocked, so you can tune a site before enforcing. Off disables the WAF for that site.
- Our own rules
Scanner signatures, secret files such as
.envand.git, path traversal, encoding tricks and request smuggling, which the Core Rule Set doesn’t cover on its own. - Emergency rules for new CVEs
A virtual patch reaches every node while you update, like rule 10075 against PHP2Shell.
- Stack shields
8 protections for WordPress, GraphQL, source maps, open redirects, SSRF and prompt injection, each one off per path when it gets in the way.
- Exceptions and block page
Switch a rule off for a site or a path, and show blocked visitors a page with your client’s brand.
Rate limitingSlow brute force and scrapers before they cost the origin anything.
A rule matches a path and its methods, then counts by whatever identifies the client.
{"name": "Login",
 "path_prefix": "/auth/login",
 "methods": ["POST"], "key": "ip",
 "requests": 60, "period": 900,
 "algorithm": "gcra", "action": "block",
"mitigation_timeout": 900}- Up to 25 rules per site
Match a path, its methods, a header or a query parameter, with templates for login, one-time codes and APIs.
- Count by what matters
By IP, by a header such as an API key, by a cookie or by a JSON field in the body, with a sliding window or GCRA.
- Block, challenge or log
Excess requests get a 429, a proof-of-work page or just a log entry, with an optional penalty time.
Access gatePut /wp-admin behind a one-time e-mail code.
Bots and password guessing never reach the login form, and the application doesn’t change.
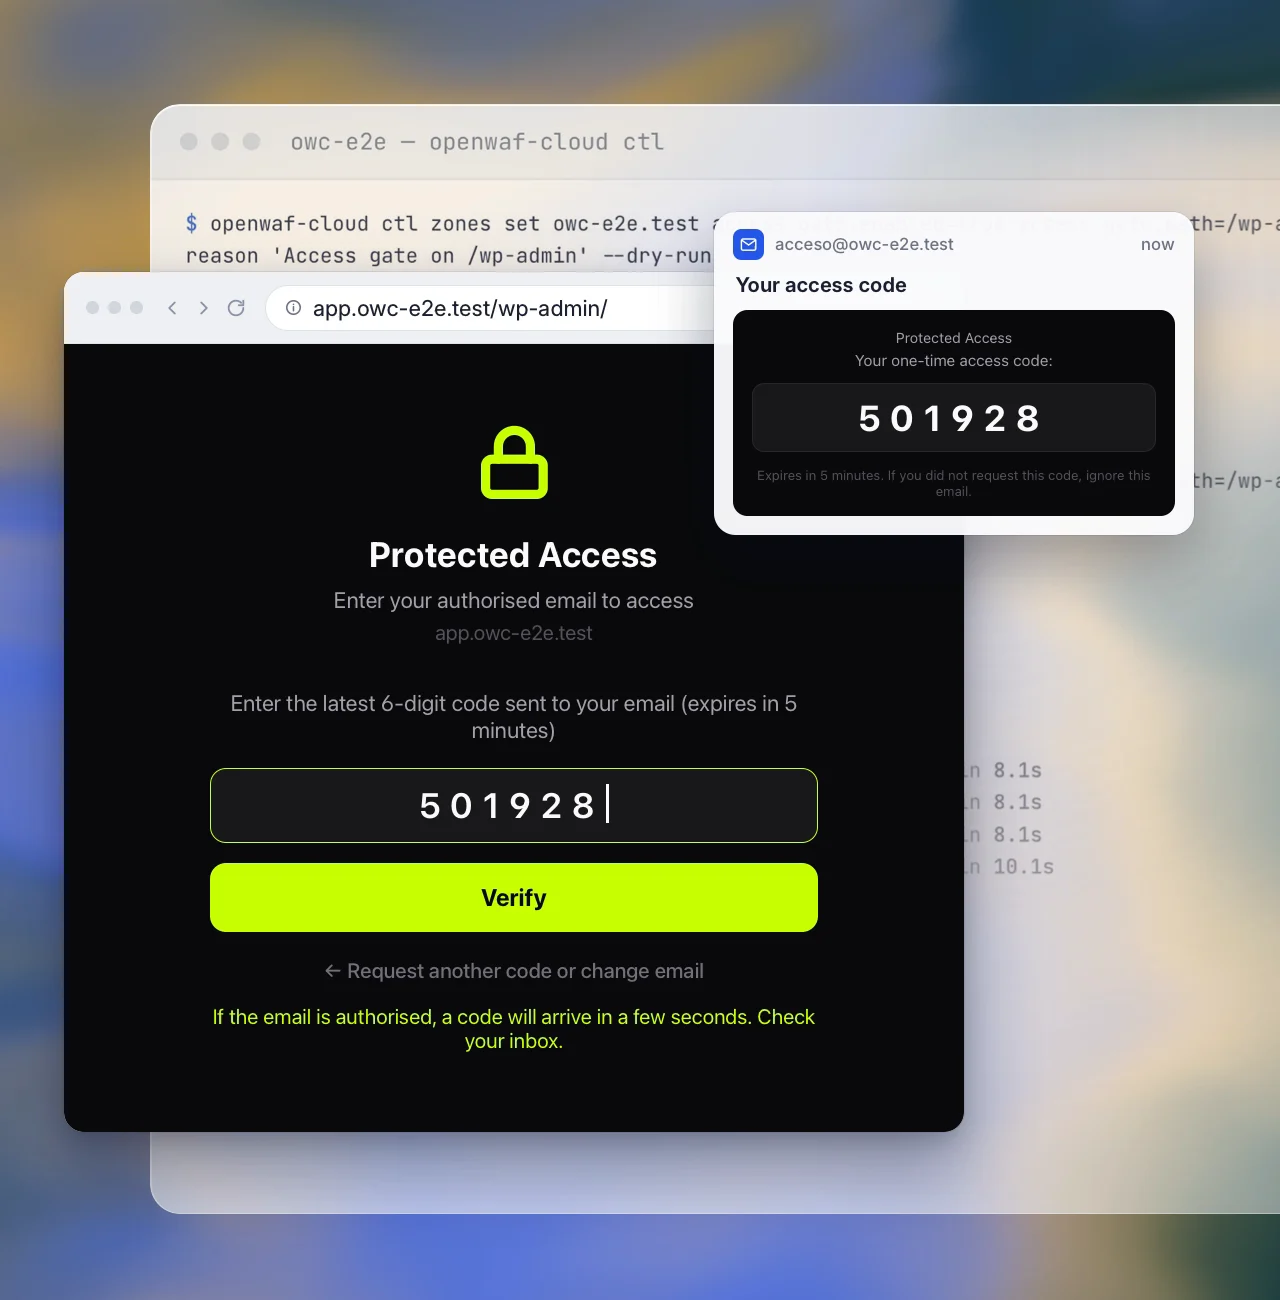
- Protect paths such as
/wp-adminRequests to a protected path are held at the edge until the visitor proves who they are.
- One-time e-mail codes
Authorised people receive a one-time code by e-mail, sent from
[email protected]. - A list of people per site
Decide who can reach each site’s admin area.
IP, country and threat-intelligence rulesChoose who can reach each site.
Single addresses, whole networks, countries or a threat-intelligence feed.
$ openwaf-cloud ctl rules add example.com \
    kind=ip ip=198.51.100.0/24 action=block \
    --reason "scanner range"
$ openwaf-cloud ctl rules add example.com \
    kind=ip ip=203.0.113.10 action=allow \
--reason "office"- Allow and block lists
Single addresses or CIDR ranges, per site.
- Country rules
Allow or block traffic by country.
- Threat-intelligence feeds
Block addresses that appear in threat-intelligence IP feeds, which are updated automatically.
Site settingsRedirects, CORS and limits, kept in one place per site.
The settings that usually end up scattered across server configs.
{"redirects": [{"host": "www.example.com",
   "status": 301, "path_prefix": "/old",
   "target": "https://example.com",
   "preserve_path": true, "preserve_query": true}],
 "cors_allow_origins": ["https://app.example.com"],
 "redirect_allow_hosts": ["example.com"],
"max_body_mb": 25, "timeout_ms": 5000}- Redirect rules
Up to 50 redirects per site, 301 to 308, keeping the path and query if you like.
- CORS allow-list
Control which origins may call the site’s APIs from a browser.
- Redirect allow-list
Limit where the site may redirect visitors, to stop open-redirect abuse.
- Request limits
Maximum request size and time-out towards the origin.
FAQ
Questions about the firewall
Can I try the rules before they block anything?
Yes. Each site has three WAF modes: active blocks, log-only records what would have been blocked so you can tune the site first, and off disables the WAF for that site.
What if a rule blocks a legitimate plugin or form?
Switch that rule off for the site or for one path. Stack shields can be switched off per path too.
What happens when a critical CVE is published?
A virtual patch goes to every edge node while you update, like rule 10075 for PHP2Shell.
Related
Keep exploring
Bots and AI agents
Let search in, keep scrapers and fakes out
Learn more: Bots and AI agents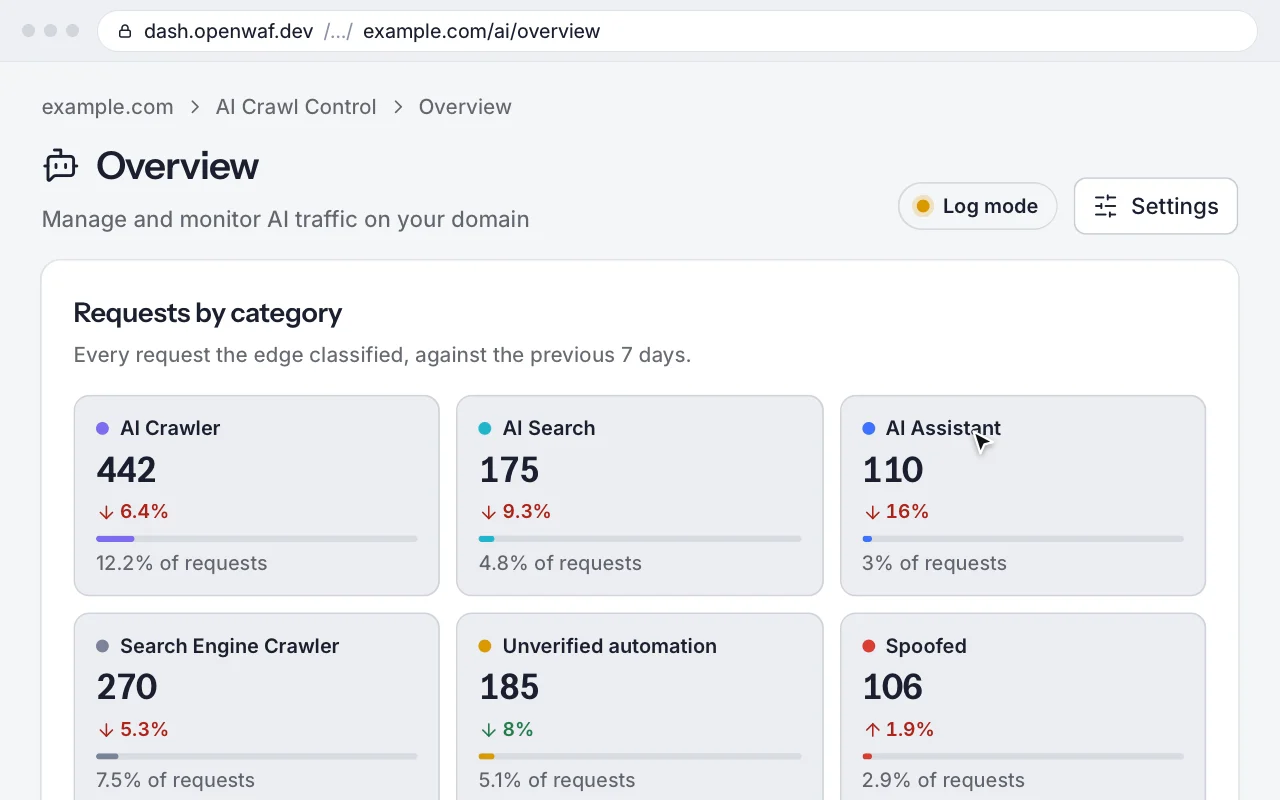
DNS, TLS and origin
Stay up without running your own DNS
Learn more: DNS, TLS and origin$ dig +short NS example.com faros.ns.openwaf.dev. polaris.ns.openwaf.dev. $ dig +short MX example.com 1 smtp.google.com.Change control
Every change on the record, and one step back
Learn more: Change control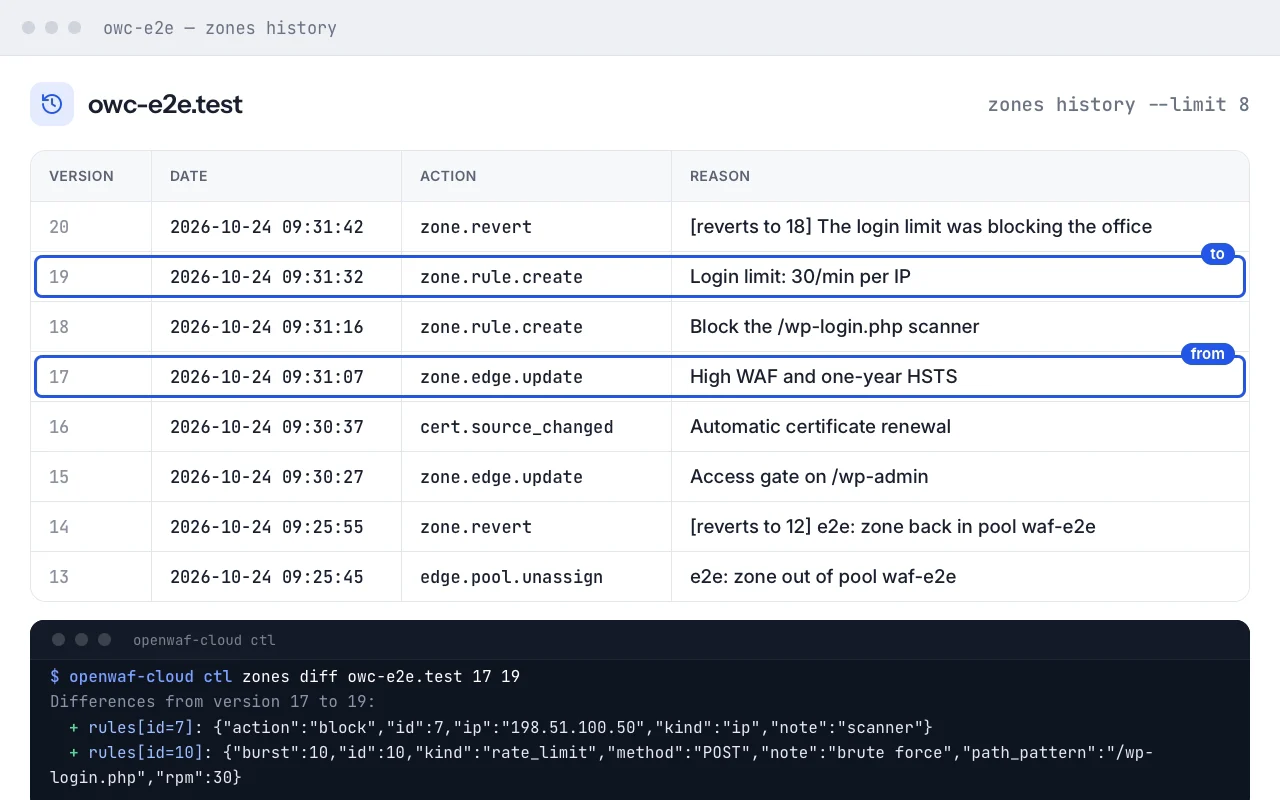
Put a firewall in front of every client site.
Free during early access. Add a domain, start in log-only mode and enforce when the numbers look right.