
DNS, TLS and origin
Your own nameservers, certificates included.
Each account has a fixed nameserver pair under ns.openwaf.dev. Delegate a domain to it, or keep your DNS and point hostnames at OpenWAF with a CNAME. Certificates are issued and renewed for you, and new domains verify the origin’s certificate with Full (strict).
Your own nameservers, certificates included
Each account has a fixed nameserver pair under ns.openwaf.dev. Delegate a domain to it, or keep your DNS and point hostnames at us with a CNAME: OpenWAF proxies the hostnames you choose and issues their certificates.
Authoritative DNSOne nameserver pair for every client domain.
Delegate a domain to your pair, or keep your DNS and point hostnames at OpenWAF.
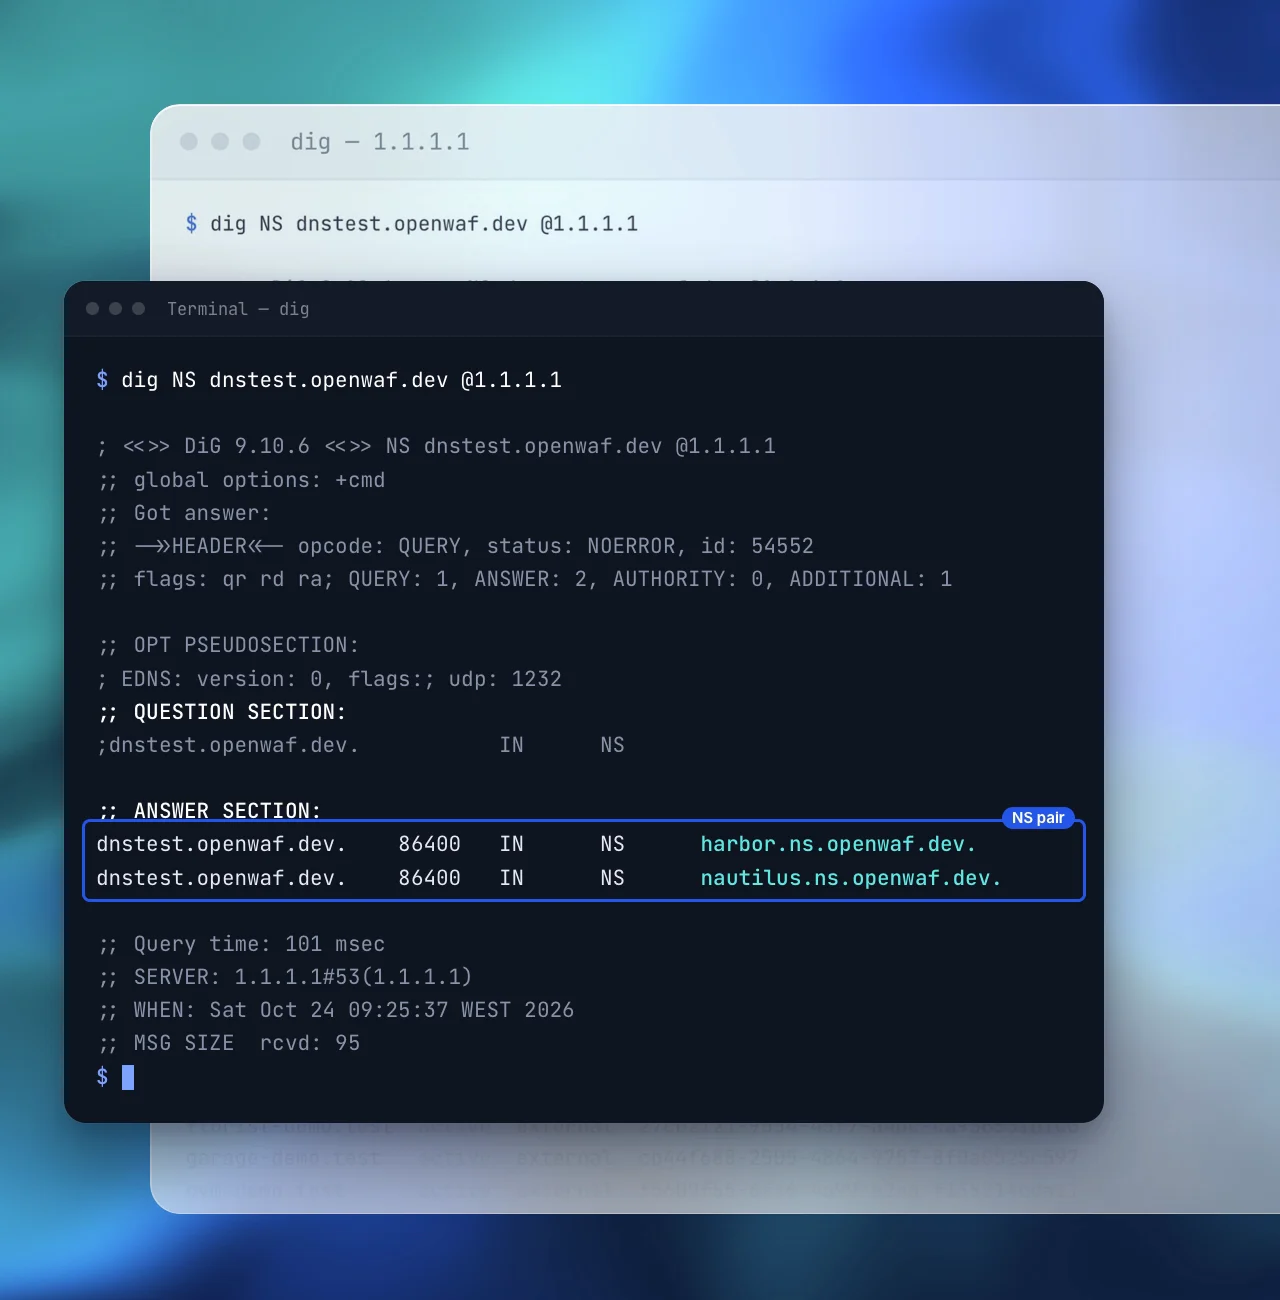
- A fixed nameserver pair
Each account has its own pair under
ns.openwaf.dev, named after navigation: faros, polaris, meridian, azimut, sextant, compass, harbor, nautilus, portolan and beacon. - Or keep your DNS
Verify the domain with a TXT record and point each hostname at OpenWAF with a CNAME or an A record.
- Health-checked answers
Edge nodes are checked every 5 seconds, visitors get the nearest healthy one, and a failed node leaves the answers in about 20 seconds.
- Hidden primary, public secondaries
The primary isn’t reachable from the Internet; public secondaries in Germany answer the queries.
- Proxied or DNS-only, per record
Choose which hostnames go through the WAF; everything else gets plain DNS answers.
- Import and edit
Import a BIND file or the domain’s public records, and edit every record type with a proxy switch.
E-mail that keeps workingMove the DNS without breaking the mail.
Moving DNS is when mail usually breaks. The dashboard checks it and sets it up for you.
example.com.  MX   1 smtp.google.com.
example.com.  TXT  "v=spf1 include:_spf.google.com ~all"
google._domainkey.example.com.
TXT "v=DKIM1; k=rsa; p=MIIBIjANBg…"- Mail check
MX, SPF with its nested lookups, DKIM and DMARC as the public DNS sees them, plus proxied mail names and conflicts.
- Provider setup in one change
Templates for 12 providers, from Google Workspace and Microsoft 365 to Amazon SES and Resend, applied as a single versioned change.
Automatic TLSCertificates that renew themselves.
TLS ends at the edge, with Let’s Encrypt or a certificate you upload.
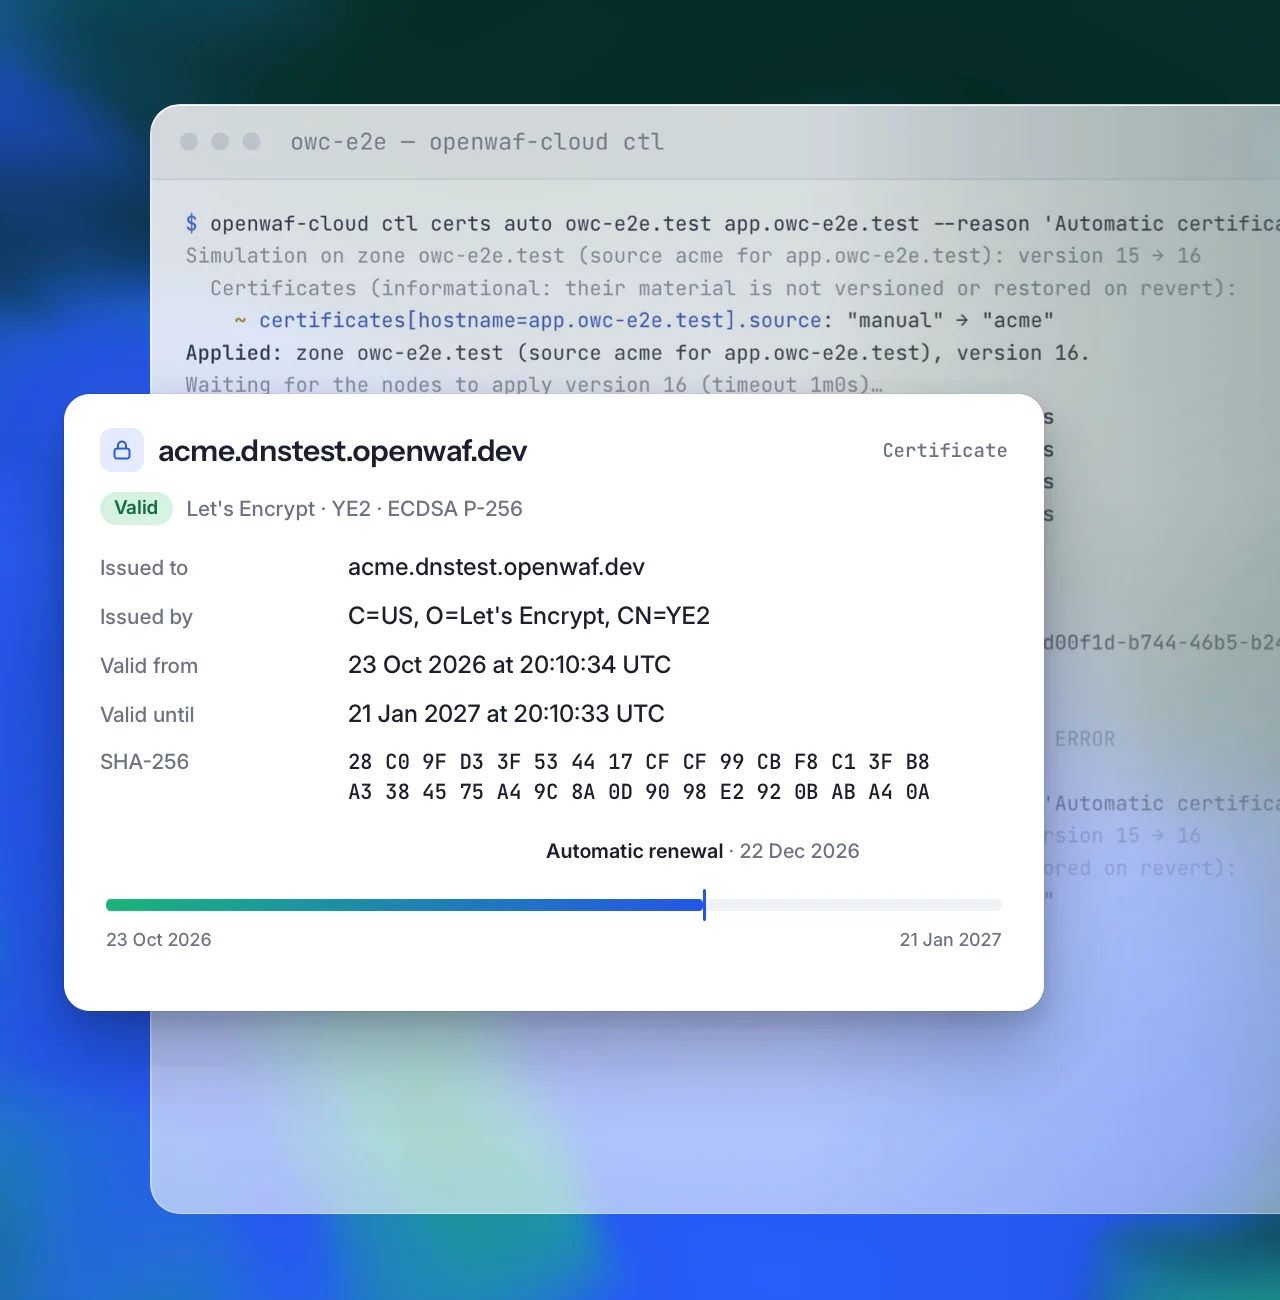
- Let’s Encrypt certificates
Issued automatically with DNS-01 or HTTP-01 validation.
- Renewed 30 days before expiry
Renewal starts 30 days before a certificate expires.
- Bring your own
Upload a certificate manually when a client needs a specific one.
- HSTS
Turn on HTTP Strict Transport Security per site.
Origin protectionEncrypt the leg to your server, and let only OpenWAF through.
Verified TLS to the origin, free origin certificates and authenticated origin pulls.
{"origin": {
  "scheme": "https", "port": 443,
  "tls_verify": "full_strict",
  "server_name": "origin.example.com",
"client_cert": true}}- Full (strict) by default
New domains verify the origin’s certificate; a mismatch is a clear 526 instead of a silent risk.
- OpenWAF Origin CA
Free origin certificates valid for up to 15 years, from a key we generate or your own CSR. We don’t keep the private key.
- Authenticated origin pulls (mTLS)
The edge presents a client certificate, so your server can refuse every connection that doesn’t come through OpenWAF.
- Post-quantum hybrid TLS
X25519 with ML-KEM-768 is preferred towards visitors and towards your origin, against harvest-now-decrypt-later.
FAQ
Questions about DNS
Do I have to change the nameservers? Can I use a CNAME instead?
Either. Delegate the domain to your OpenWAF pair and we answer all of its DNS, or keep your DNS where it is: verify the domain with a TXT record and point each hostname at OpenWAF with a CNAME (or an A record at the apex).
Where do you run?
Edge nodes in Germany and Spain; DNS servers and customer data in Germany. DNS answers are health-checked, so visitors get the nearest healthy node and a failed node leaves the answers in about 20 seconds.
Will moving the nameservers break e-mail or other services?
Not if the domain has the same records as before. Records that aren’t proxied, like MX for e-mail, are answered exactly as you define them. The dashboard checks MX, SPF, DKIM and DMARC as the public DNS sees them, and sets up mail for 12 common providers in one change.
Bring your domains without breaking mail.
Free during early access. Add a domain: we detect its existing records, check its mail and give you the nameserver pair to set at the registrar.